
Connect your organization's identity provider so learners can enter Honen using their existing sign-in. Honen offers presets for Google Workspace, Microsoft Entra ID, Okta, Auth0, and Keycloak, plus Generic OIDC.
You need Manage integrations and Manage identity providers permissions in a team workspace. Your identity administrator must be able to register the provider application.
1. Register Honen with your provider
- Open Organization → Integrations → Identity & SSO.
- Under OpenID Connect, copy the OIDC callback URL.
- In your provider, create a confidential web application using the authorization-code flow.
- Register the copied callback as the application's redirect URI. Use the exact value shown in your workspace.
- Include the
openid,profile, andemailscopes. Configure a stable subject identifier and the learner email used in your workspace. - Obtain the application's issuer URL, client ID, and client secret. Assign the intended test user or audience in the provider.
For the Honen production host, the callback is https://honen.com/api/auth/sso/oidc/callback. Copying it from the screen keeps your setup aligned with the environment you are using.
2. Add the connection in Honen
- Choose Add OIDC connection.
- Enter a Connection name, such as “Northstar workforce.”
- Select the matching Provider preset.
- Enter Issuer URL, Client ID, and Client secret from the provider application.
- Review Scopes, which starts with
openid profile email. - Choose Default member role and whether to use JIT provisioning.
- Review Allow account-wide session requests according to your identity rollout plan.
- Choose Add connection.
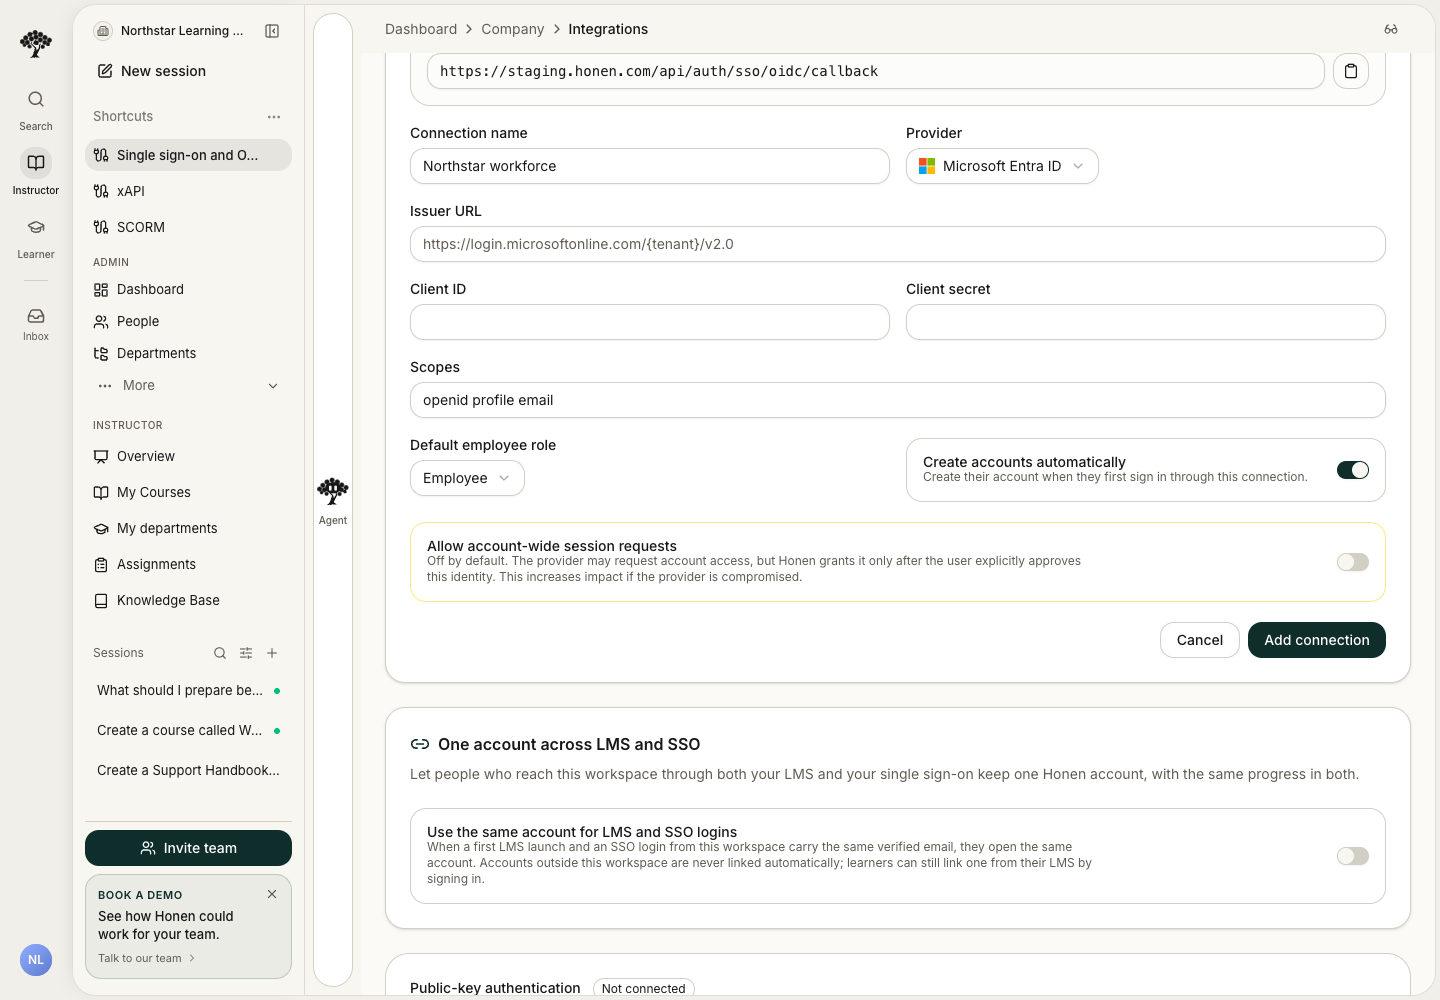
The screenshot shows the setup fields before credentials are entered. Supply the values from your own provider application when configuring your connection.
Built-in provider presets and examples
Choose the matching Provider in Add OIDC connection. These presets use the same Honen callback and authorization-code flow. Replace every example value with your organization's provider application values.
| Built-in preset | Example issuer | Provider setup to check |
|---|---|---|
| Google Workspace | https://accounts.google.com |
Create a web OAuth client. Configure the managed email domains used by learners. |
| Microsoft Entra ID | https://login.microsoftonline.com/11111111-2222-3333-4444-555555555555/v2.0 |
Use your tenant ID. Copy the Application client ID and client-secret value. |
| Okta | https://northstar.okta.com or https://northstar.okta.com/oauth2/default |
Copy the exact issuer from the authorization server assigned to the application. |
| Auth0 | https://northstar.us.auth0.com/ |
Use your Auth0 tenant or configured custom issuer. Register a Regular Web Application. |
| Keycloak | https://id.northstar.example/realms/learners |
Use the intended realm and a confidential OIDC client. |
| Generic OIDC | https://id.northstar.example |
Copy the exact issuer from the provider's discovery document. |
For every preset, enter the application's Client ID and Client secret in Honen. The issuer must match the provider's discovery document, including any required path or trailing slash. Honen reads the authorization, token, and public-key endpoints from that document. A preset does not create the provider application or assign its users.
Prepare Microsoft Entra ID
Use your organization's tenant-specific issuer, client ID, and client secret. The issuer contains the tenant ID, rather than common or organizations. Keep the Honen callback URL as the registered redirect URI, even when learners start on your workspace subdomain.
Configure the application to supply the user's email, name, tenant ID, and object ID in its ID token. The email must match the person's Moodle and workspace email for email matching. A username or display name alone is not an email match.
Entra does not normally supply the generic email_verified claim. If your organization trusts its directory emails, select Microsoft Entra SSO under One account across identity providers. Otherwise, configure a supported verified email claim with your identity administrator. Honen still validates the token signature, issuer, audience, expiry, and login nonce.
Before rollout, test a learner who already uses Moodle and a learner signing in for the first time. Confirm their member records, course access, groups, and progress.
3. Test the complete learner sign-in
- In the saved connection card, choose Test sign-in.
- Sign in as the intended provider test user.
- With trusted email matching enabled, confirm that the existing workspace member opens without another connection step.
- Otherwise, complete account linking if prompted.
- Confirm the intended Honen workspace and member role.
- Open a course assigned to that learner and return to the workspace.
- Check the connection's Last login information.
- Repeat the sign-in from your workspace's Honen subdomain.
Test both a new learner and an existing Honen account when both will be part of your rollout. Coordinate this with your identity administrator so the provider's application assignment and Honen's access policy match.
4. Maintain the connection
- Enable or pause sign-in: use the switch on the connection card.
- Rotate the client secret: create the replacement in your provider, choose Rotate secret in Honen, enter Replacement client secret, and select Save secret. Test sign-in again before retiring the old provider secret.
- Adjust account-wide requests: use the connection's Account-wide requests setting according to the approved rollout scope.
- Retire the connection: plan the replacement sign-in route, then use Delete when that connection should be removed. Review active-session handling as part of your offboarding process.
Review SSO and identity to plan provisioning, account linking, and session scope. For a portal that signs its own launch assertions, use Signed JWT.